User access
The User access tab centralizes the workspace permission matrix. It complements the environment roles (see Workspace members) with fine-grained control.
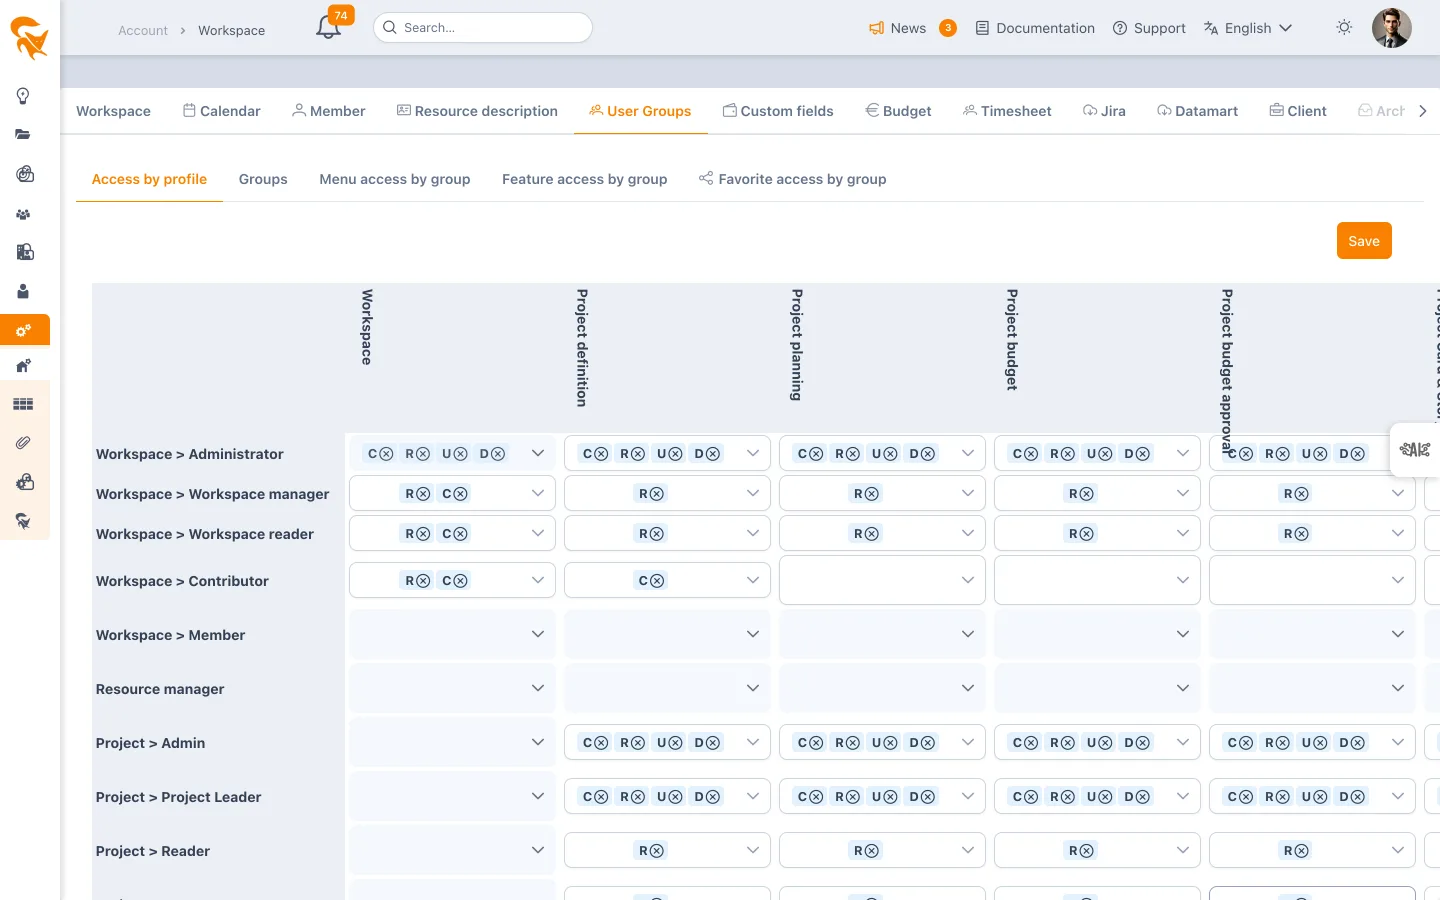
Settings → Workspace → User access
The screen exposes six sub-tabs.
Profile access
The role × feature × operation matrix. For each FoxPlan role (project manager, contributor, reader, resource, etc.), you choose the allowed operations (View, Create, Edit, Delete) on every feature (Card, Story, Budget, Risk, Decision, etc.).
- The "reader" and "resource" roles are restricted to read operations.
- Some cells are locked by design (e.g. you cannot disable reading the name of a project you have access to).
- The Save button persists the changes.
This is the screen to fine-tune standard roles to your organisation.
Clients screen
The Clients column sets access to the Clients module (clients, contracts, pre-invoices) with two kinds of rows:
- workspace roles (Workspace > …): the rights granted apply to all clients of the workspace;
- client roles (Client > Client leader, Client > Member, Client > Reader): the rights apply only to the clients the person is a member of, with that role.
A client is visible with View; creating, editing and deleting a client or its contracts require Create, Edit and Delete. A person's rights add up: those of their workspace role, plus those of their role on the client. The workspace administrator always has every right (greyed-out row).
By default, the client leader and members have every right on their clients, the reader can only consult, and the other workspace roles only see the clients they are a member of. Client roles are meaningless on the other screens: their cells are empty there. In the Clients module, everyone only sees the buttons they can use: without the edit right, the client record and the contract are shown read-only.
What the interface hides automatically
- "New project" button: only shown to people allowed to create a project in the space (Administrator and Project creator by default).
- Portfolios and Resources menus: reserved for full licences. Someone on a contributor licence keeps the "Me" space (dashboard, timesheet, cards).
- No project available: a member who sees no project and cannot create one gets a message inviting them to contact the platform administrator, with their first name, last name and email address.
Groups
User groups let you apply additional rights to a subset of members, regardless of their role. Examples: "Executives", "PMO", "Innovation team".
For each group:
- Name the group
- Add its members
- Configure its rights in the Menu access, Feature access, Shared favorites and Project templates sub-tabs
A group can be linked to AD groups: with SSO provisioning, its members then follow the directory at each sign-in, and an AD badge marks them in the list — see User provisioning and AD groups.
Menu access by group
For each group, choose which menus are visible and accessible. Useful to hide the Portfolio menu from purely operational contributors, or to expose an arbitration menu only to the executives.
Modules unticked when the space was created (Risks, Decisions, Project status…) appear unticked for every group: tick them again to bring them back. A member who does not belong to any group yet follows the rules of the All users group.
Feature access by group
Refine the features available to the group's members: reporting, exports, arbitration mode, Datamart view, etc. Combined with profile rights, it offers full control.
Create project templates is the exception: this feature is closed by default. Enterprise and workspace administrators always have it (their box is ticked and locked); to open it to other people, tick it for one of their groups. It drives the Project template choice of the creation wizard and the "as a template" option of duplication; the server rejects any template creation without this right.
Create Scrum projects is open by default: untick it for a group so that its members can no longer create Scrum projects. The Scrum type then disappears from the creation wizard, Scrum templates included, and the server rejects the creation of a Scrum project, the duplication of a Scrum project and creation through the AI assistant. Existing Scrum projects are not affected.
Shared favorites by group
Share favorite views (filters, Kanban boards, configured Gantt views) inside a group. When an administrator publishes a view, every member of the group finds it in their favorites.
Default dashboards
Every workspace receives four shared favorites right away, one per dashboard type:
| Favorite | Screen | Content |
|---|---|---|
| Project dashboard (default) | A project's dashboard | Progress, weather, budgets, work by resource, deadlines, cards |
| Project portfolio dashboard (default) | A project portfolio's dashboard | Number of projects and resources, budgets, projects weather, workload, risks |
| Team dashboard (default) | A resource portfolio's dashboard | Number of projects and resources, planned / actual / forecast work, staffing |
| My dashboard (default) | The "Me" dashboard | My workload, my cards, my deadlines, my tasks |
They are assigned to the three default groups (All users, Environment administrators, Enterprise administrators). An empty dashboard — brand-new portfolio or team, project without blocks, "Me" space never customised — displays them right away; everyone else finds them in their favorites menu, read-only.
They are favorites like any other: their owner (a workspace administrator) can edit them from the dashboard, and the Shared favorites sub-tab lets you remove them from a group, assign them to others or delete them. A deleted default favorite is not recreated.
For shared favorites, the default groups follow the workspace members in real time: a person added to the workspace receives them immediately, without waiting for an administrator to open the groups screen.
Project template access by group
Open project templates to whole groups, instead of adding each person as a member of each template.
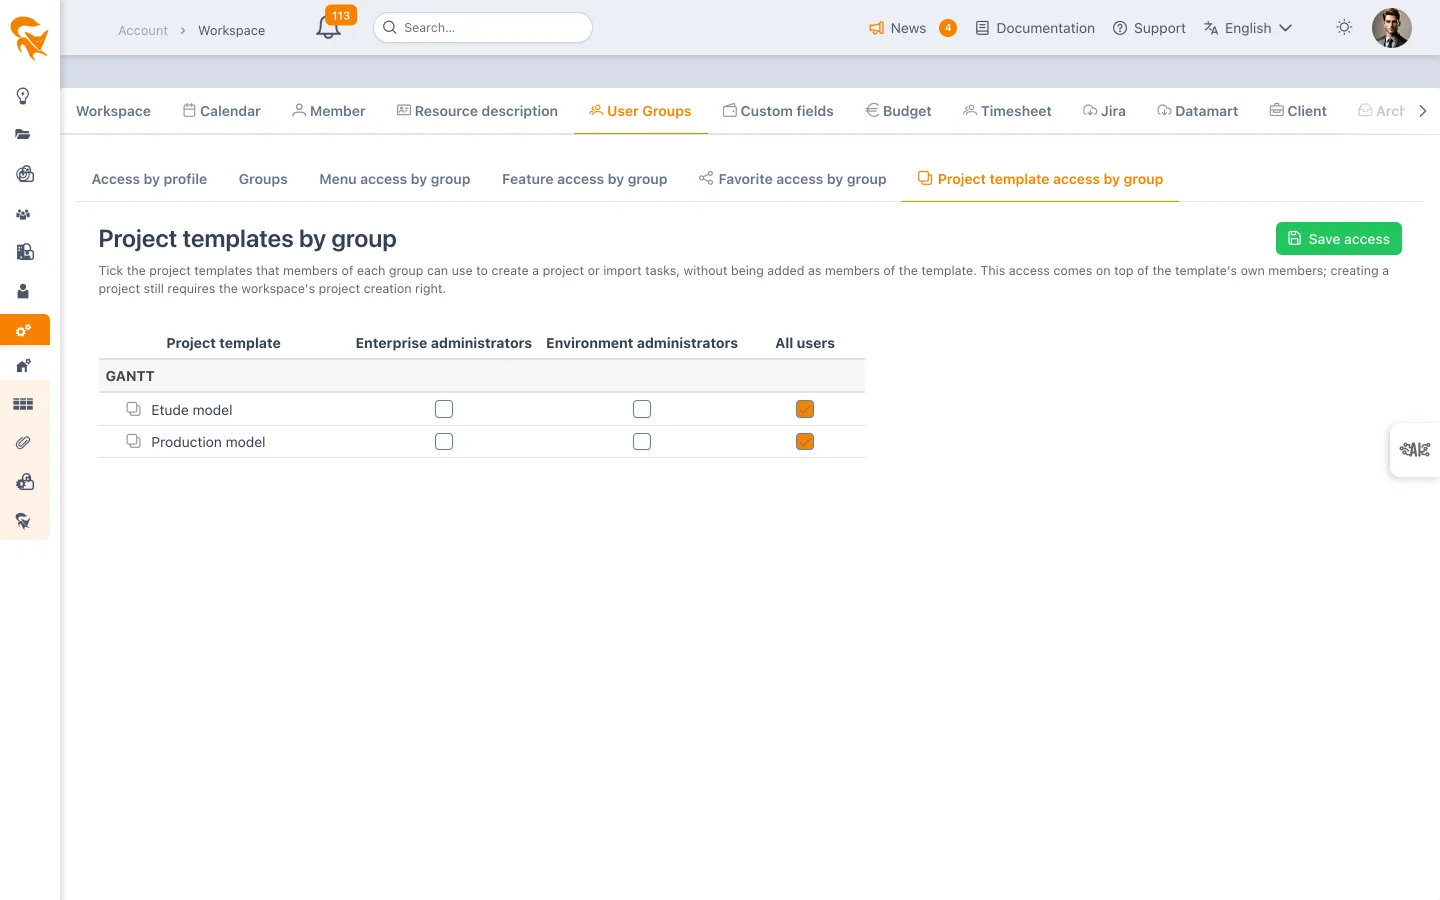
The matrix lists the workspace's templates, grouped by type (Gantt, Kanban, Scrum), with one column per group. Tick a box so the group's members can use the template, then click Save access.
Members of an authorized group can then:
- create a project from the template via New project → Or create from a template (see Project management);
- import the template's tasks into a project of the same type from the planning (see Planning).
Good to know:
- Access adds up, it never removes. Template members keep their access whether or not they belong to a ticked group; workspace administrators always see every template.
- Using is not editing. The group lets people start from the template, not open or modify it: to change a template, you must be a member of it with a suitable role.
- The creation right is still required. To create a project from a template, the person's workspace role must allow project creation (see Profile access). Importing tasks happens in a project on which they already have edit rights.
- Only available (non-archived) templates are offered when creating a project. A deleted or archived template disappears from the matrix, and its access entries are purged on the next save.
- As with shared favorites, the default groups (All users, Environment administrators, Enterprise administrators) follow the workspace members in real time: ticking All users opens the template to anyone added to the workspace later.
- Start by defining profile roles as the "baseline".
- Use groups to handle exceptions without breaking the baseline.
- Avoid multiplying groups: fewer than 10 groups stays manageable.
See also
- Workspace members — global roles
- Project members — project-level roles